PiSecurityCheck:an Android tool for your security
An application developed to enhance the inner security of your webserver. Find out with just 2 taps, if your webserver is vulnerable to Sloris attack or Layer 7 DDoS attack!
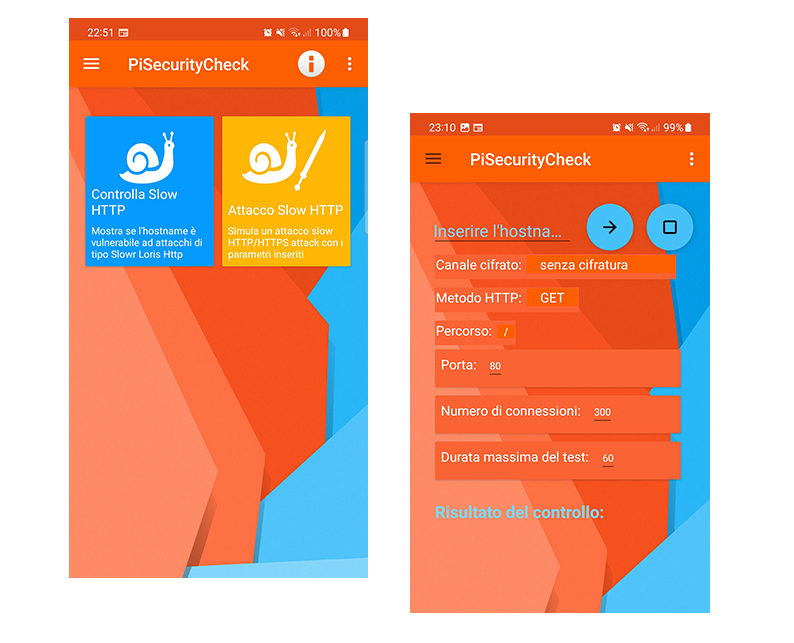
An application developed to enhance the inner security of your webserver. Find out with just 2 taps, if your webserver is vulnerable to Sloris attack or Layer 7 DDoS attack!
Spot vulnerability and check immediatly if the availability of your website can be destroyed by just a couple of HTML request. And if you want to double check it, you can also emulate a DDoS to your own website. Play at your own term.
The Slowloris HTTP attack exploits the normal behavior of a webserver that waits for the end of an HTTP request indefinitely (or the expiration of a preset timeout) before closing the connection. By default a web server allows slow connections to send information with a low transmission rate due to degraded communication channels.
The final goal is to exhaust all the resources of the server by setting up multiple dumb connections that transmit data at a very low rate. The POST method is used in the request with the header field ”Content-Length”(normally used to announce to the recipient the dimension of the body of the request) set to a very large number. Doing so the server would keep the underlying connection open, waiting for the useless connection to finally transmit all the body content announced in the first place inside the header. From time to time, the attacker sends a small piece of information (usually one or two bytes), just to be sure that the recipient will not close the connection, so the resources would be kept busy.
The feature has been implemented with a start and a stop button. Based on the selected method, the application would open a number of sockets (the default value is set to 300 and it is not possible to open more than 1024 parallel connections) with a timeout value specified by the user (the maximum value for the timeout is 120 so that after this time period all the connections are closed). Every socket is attached to a concurrent thread. If for any reason the thread crashes, the socket fails, or is interrupted by the server, the application automatically set up a new thread with a new socket and tries again to establish the connection.
The aim of the application is to easily check if the webserver is vulnerable to a very annoying DDoS attack. Moreover the application will be implemented with more functionalities in order to give user the highest amount of informations easily aknowledgeble by everyone, even non-technical personnel
satisfaction
User friendly